Brian Sims
Editor
Brian Sims
Editor
THE INFORMATION Commission’s Office (ICO) has issued a reprimand and an Enforcement Notice to the Metropolitan Police Service after finding that the latter’s officers and staff shared personal information using an unapproved third party retail crime intelligence-sharing platform without appropriate data protection safeguards, governance or oversight.
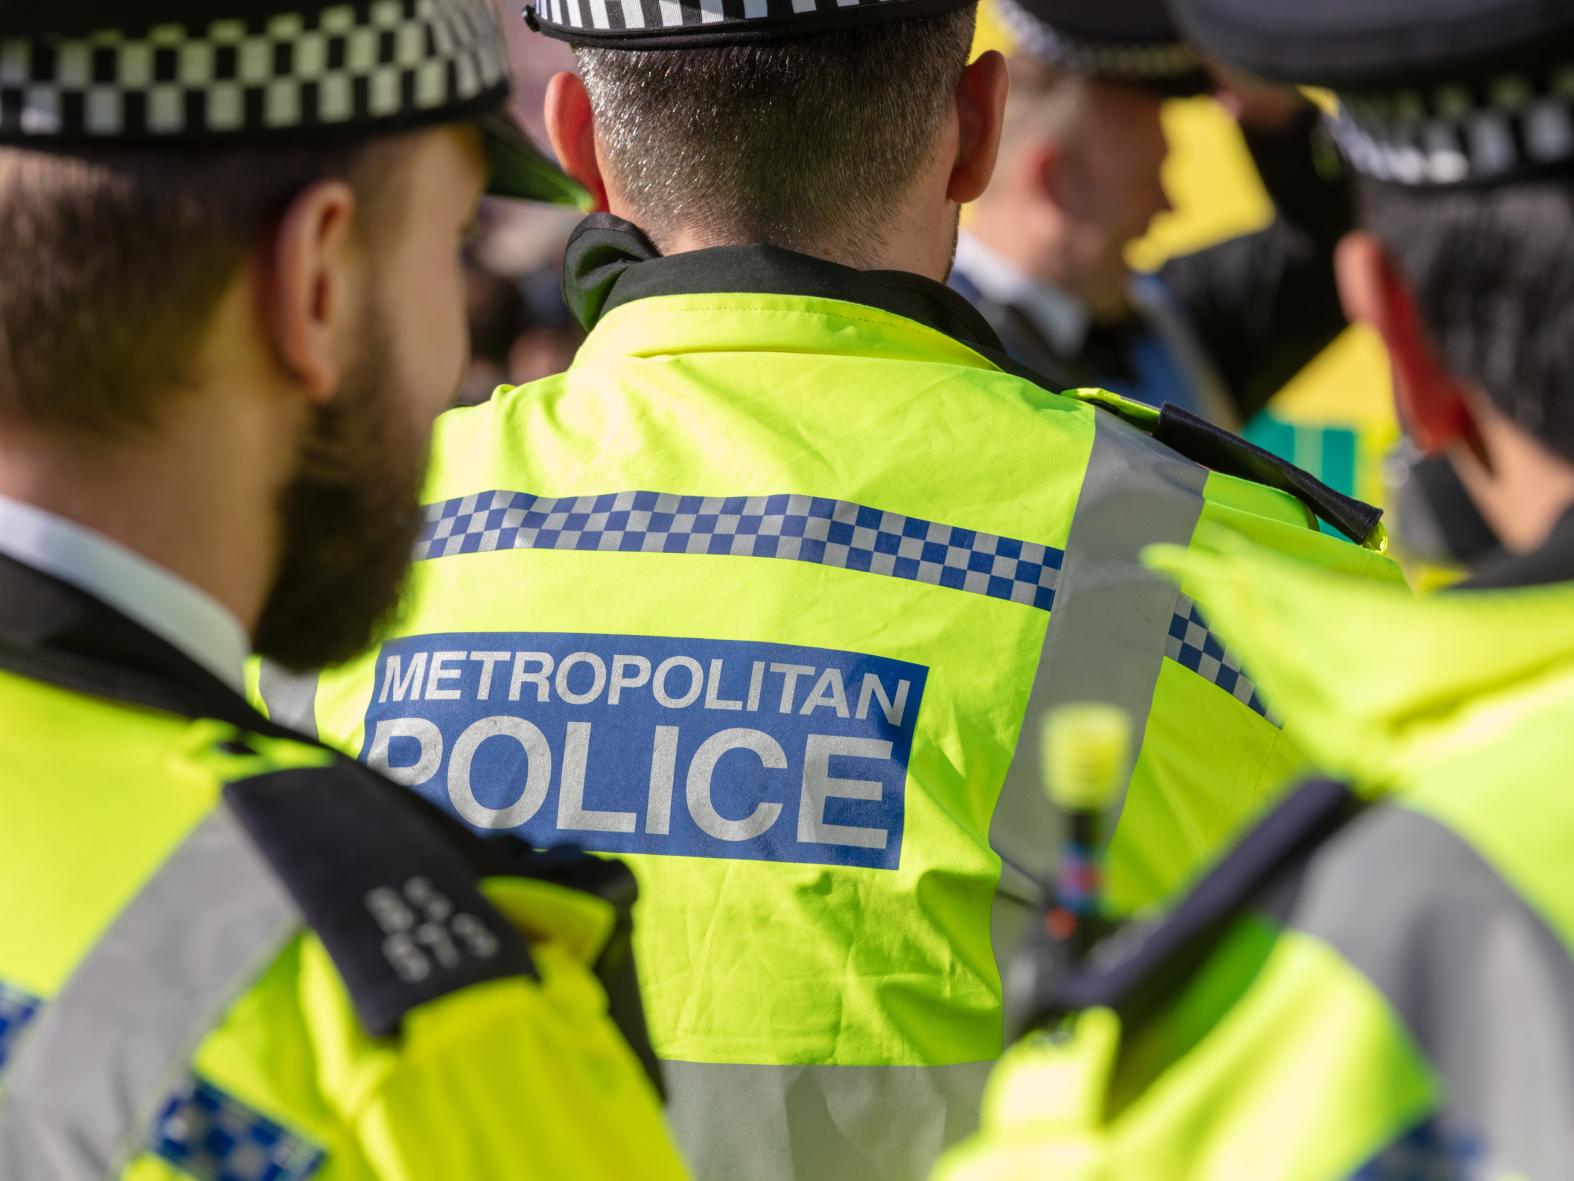
The ICO’s investigation found that Met officers and staff used the platform between March 2023 and September 2024, despite it not being formally approved for use by the police service. Around 500 accounts were created, with 375 actively used for policing activities.
The investigation found that, between January and September 2024, the personal information relating to 179 individuals (three of whom were under the age of 18) was uploaded to the platform as part of efforts to identify individuals suspected of shoplifting. This included names, dates of birth and, in a small number of cases, home addresses.
The ICO found that the Metropolitan Police Service:
*unlawfully processed personal information without the individual’s consent and where sharing was not necessary for law enforcement purposes
*failed to implement appropriate technical and organisational measures to protect personal information and ensure that assessment and approval processes for third party technologies were followed
*failed to complete a data protection impact assessment before undertaking high-risk processing
*continues to fail to implement appropriate measures to ensure that only approved third party technologies are used to process personal information
Robust safeguards
David Doodson, the ICO’s head of investigations, explained: “Police forces hold large volumes of sensitive personal information and must have robust safeguards in place to protect it.”
Doodson continued: “While new technologies can deliver significant operational benefits, organisations cannot allow innovation to outpace their data protection responsibilities. Before introducing new systems or platforms, they must properly assess the risks, put appropriate safeguards in place and ensure effective oversight.”
Further, Doodson noted: “This action should send a message across the policing sector and beyond: if you’re using new technology to process people's information then you must do so lawfully, transparently and with appropriate governance from the outset.”
In a word of warning, Doodson affirmed: “Where organisations fail to protect people's information, we will take action. Our role is not only to hold organisations to account, but also to drive improvements and promote the standards people have a right to expect.”
Improvements implemented
In reaching its findings, the ICO acknowledged that the Metropolitan Police Service suspended use of the platform in September 2024 and implemented a range of improvements and safeguards prior to reintroducing it in January 2026.
These safeguards included stronger governance arrangements, additional staff training, formal contractual controls and the completion of a data protection impact assessment.
However, the ICO concluded that regulatory action was still required in order to address wider governance concerns relating to the use of third party technologies by the Metropolitan Police Service.
The Enforcement Notice requires the Met to strengthen its approach towards identifying, assessing and approving third party services used to process personal information. The Met must also review its controls, improve governance processes, enhance staff awareness and regularly test the effectiveness of the measures it has in place.
The Metropolitan Police Service is required to provide the ICO with periodic updates on its implementation of the requirements as set out in the Enforcement Notice.
*Further information is available online at www.ico.org.uk
Western Business Media Limited
Dorset House
64 High Street
East Grinstead
RH19 3DE
UNITED KINGDOM